Why is my Windows Hello logon reported as Single Factor authentication?
Table of Contents
The problem
Last week I was investigating Azure AD sign-in logs to improve security and multi-factor sign-ins. By filtering all sign-ins to show only single-factor authentication I’ve got my starting point. The filter showed more single factor authentication than expected. The endpoints in this tenant are configured for Windows Hello for Business so i did expect these logons as multi-factor ones instead of single-factor authentications.
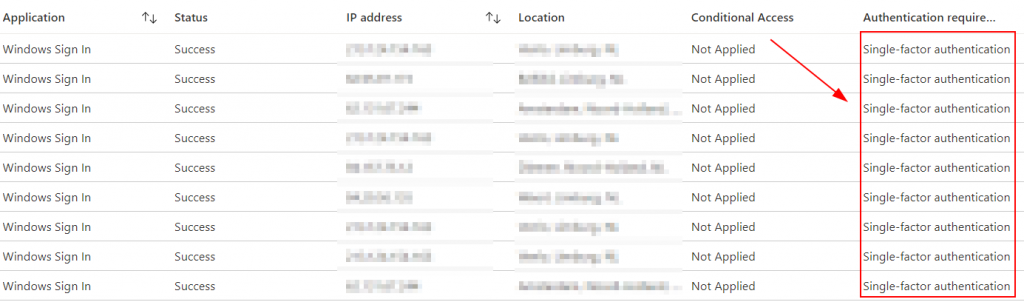
I had to make sure these sign-ins where not using username/password. Authentication details shown that the user was using Windows Hello. So, a i have a valid PRT (Primary Refresh Token) and so a claim. Then why did my sign-in reported single factor?
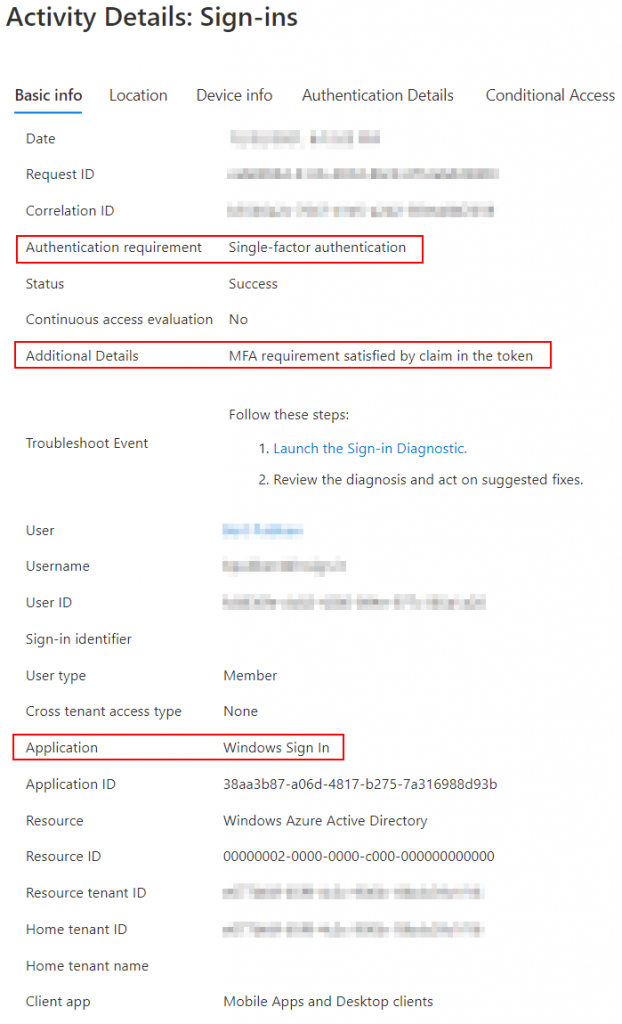
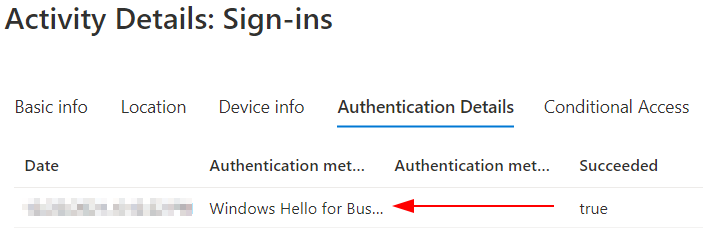
At this point Rudy Ooms was able to reproduce the issue in a different tenant. We started investigating why and found it!
Where did we go wrong?
Early in the Azure Multi-Factor days most people configured Per-user MFA. This can be set to enabled, disabled or enforced.
-
When you have disabled per-user MFA. You will NOT BE required to have MFA, so single-factor it is.
-
When you have disabled per-user MFA and you are using Windows Hello, you are making use of the “Strong Windows Hello Authentication”
-
When you have enforced per-user MFA, you will BE required to have MFA, so multi-factor it is.
-
When you have enforced per-user MFA and you are using Windows Hello, the MFA requirement is already satisfied by the claim in the token
Probably, when using a older tenant or having Azure AD identities which do exist for over a few years they could still be configured with Per-user MFA. Maybe u forgot to disabled it while migrating to Conditional Access policies?
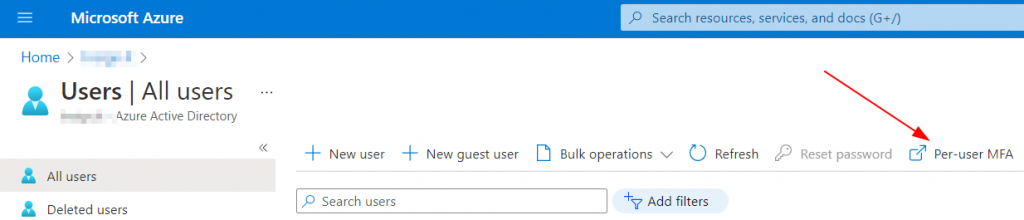
Open up Azure AD -> Users -> Per-User MFA
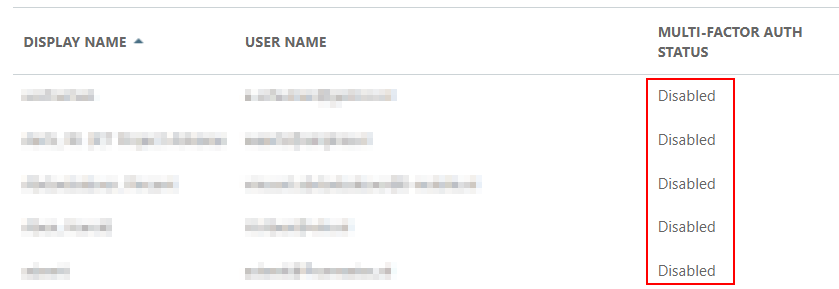
Check if your users have enabled, enforced or disabled MFA status. Users who have disabled MFA will report a single-factor logon! Users who have enforced MFA will report a multi factor logon! Even while using Windows Hello!
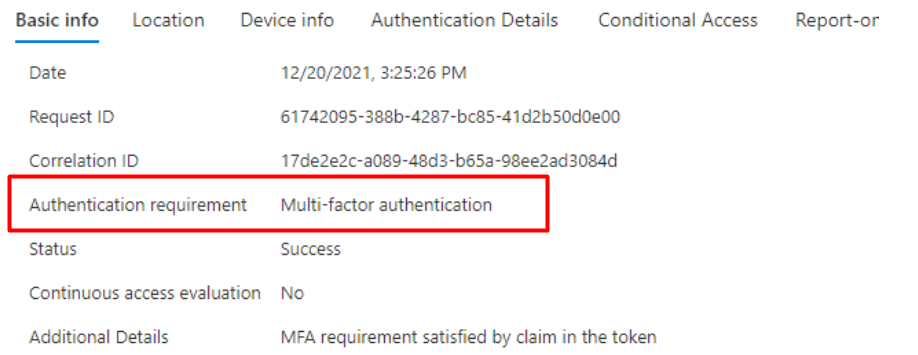
To be clear. If MFA status is enforced your sign-in reports will show multi-factor like below.
What should i do?
It’s not a big problem to have both enabled but this can be confusing. Maybe a user still receives MFA prompts while the Conditional Access policies do not require one. You should have a single pane of glass for monitoring and therefor its recommended to only use Conditional Access.
Big thanks to Rudy Ooms! Check his blog post about MFA/CA to!
Written by Joey Verlinden
Back to all articles