What happens if you lock-out your Azure Tenant?
Table of Contents
- How do you lose access?
- Prevent losing access (Break Glass)
- What if even my Break Glass admin has no access anymore?
- Microsoft to the rescue!
Have you ever wondered what to do when you lost admin access to your Tenant? Have u got a panic plan or any idea how to act when there’s absolutely no admin access to your tenant anymore? I’ll tell you about this based on my own (recent) experience.
How do you lose access?
There are many reasons why you can lose admin access to your tenant. These are a few things what can happen:
- Configuration mistake (Conditional access policy)
- Lost access to Multi Factor (MFA) device
- Azure MFA service having troubles
- Phone network unavailable (MFA SMS/Voice)
- Administrator left the organization
- Mad admin who removed other admin (roles) or disabled their accounts
Prevent losing access (Break Glass)
Microsoft advises to create at least 2 break glass admin accounts with different authentication methods. It is possible to separate both on MFA methods. Like one is using a OTP code and the other one is using a (FIDO2) security key for example. In this case you are still dependent on the Azure MFA service. It’s in fact a risk..
While we always want admin accounts to use MFA, Microsoft advises to have at least one (global) admin who is excluded from all MFA policies and thus can logon with a username and strong password. I know, it’s contradictory but losing all access is probably worse. Your identity Protection score will suffer from this and generate an advise to configure MFA. Ignore this one cause it is by purpose.
Best practices for Break Glass
-
Create two or more emergency access accounts. These accounts should be cloud-only accounts that use the *.onmicrosoft.com domain and that are not federated or synchronized from an on-premises environment.
-
The emergency access accounts should not be associated with any individual user in the organization.
-
The authentication mechanism used for an emergency access account should be distinct from that used by your other administrative accounts. For example, if your normal administrator sign-in is via on-premises MFA, then Azure AD MFA would be a different mechanism.
-
The device or credential must not expire or be in scope of automated cleanup due to lack of use.
-
You should make the Global Administrator role assignment permanent for your emergency access accounts. Exclude the account from any PIM or time based access requirement.
-
Store the passwords in a secure way or lock! Prevent easy access to these passwords! Do not store the passwords of both accounts in the same locker. Probably keep them in a digital (secured) password tool in case the physical location is not accessible.
-
Make use of a strong (random) password with at least 16 characters.
More information on Break Glass / Emergency Access can be found here.
What if even my Break Glass admin has no access anymore?
Unless you have a Break Glass account, there are still situations where these accounts are not available. For example if an admin removed the Break Glass accounts, removed their roles, disabled the users, reset the password. Maybe created a new CA policy and forgot to exclude the Break Glass accounts?
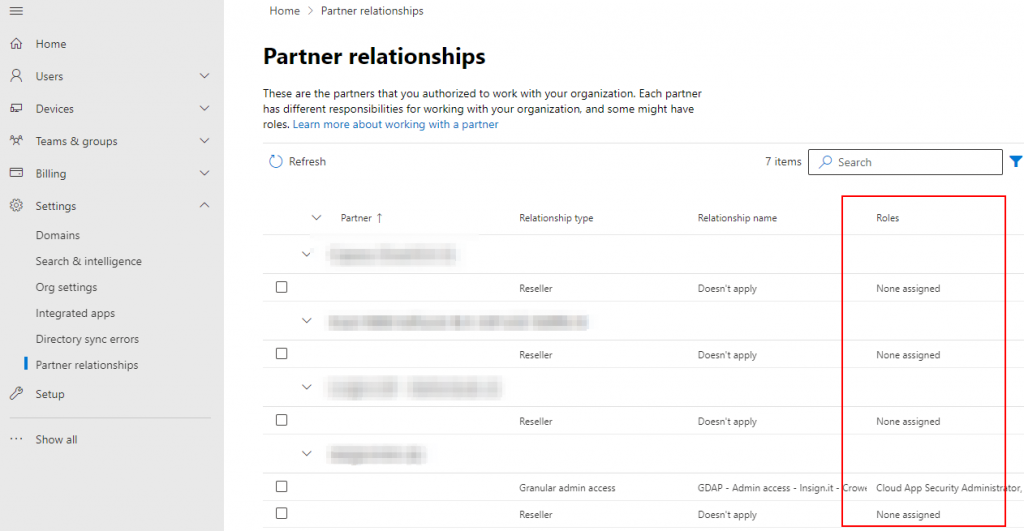
Most organizations have a MSP or CSP partner for some technical support and/or a reseller who delivers licenses to your organization. The old DAP relationship (partner relationship) mostly comes with Global Admin and Helpdesk Admin roles. Then check if you have a partner with those roles. They probably still have access and are able to support you.
https://admin.microsoft.com -> Settings -> Partner relationships
Microsoft to the rescue!
Update: Because of confidentially the process/steps are removed from the blog.
But what if there’s absolutely no access anymore? Your partners are unable to support you on this!? What now!? Then, there’s always Microsoft to the rescue! And this is exactly what I experienced a while ago. Brace yourself because this can take a few days!
Microsoft will verify your identity first, to make sure you are the right person in this situation. I am not allowed to share the process anymore, because of security reasons. As soon as your identity is verified by Microsoft, your ticket will be hand over to a support engineer who can solve the tenant lock-out by for example reverting a change.
Written by Joey Verlinden
Back to all articles