Implement (Always On) Azure VPN Gateway, Deploy Azure VPN Client and VPN profile via Intune
Table of Contents
- Create Virtual Network Gateway
- Azure VPN Enterprise App
- Point-to-site configuration
- Deploy the Azure VPN client via Intune / Endpoint Manager
- Prepare VPN Profile config
- Deploy VPN profile via Intune / Endpoint Manager
- Endpoint – User Experience
- Connection monitoring
It was Q4 2020 when I was asked to design a new Modern Workspace concept. The customer had no on-premises hardware/resources and wanted us to migrate everything into Azure. Because of the services they where using, a VPN connection to Azure was then required. Different options passed trough my mind but I decided to go for Azure Virtual Network Gateway. I really wanted this because the Azure AD identity provider support for authentication.
The endpoints are Azure AD joined, deployed via Autopilot and managed by Intune. We picked Azure VPN client for the connection and deployed a VPN profile in it via Endpoint Manager (Intune). Are u curious how it’s done? Continue reading!
Note: Most settings are default cause these are good enough for this demo and/or regular organizations. Depending on the bandwidth, total connections and/or speed requirements these settings can be different.
Create Virtual Network Gateway
- Create a resource group in Azure and click Create.
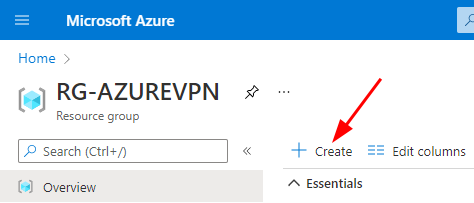
Create resource
2. Search for Virtual network gateway, click Create.
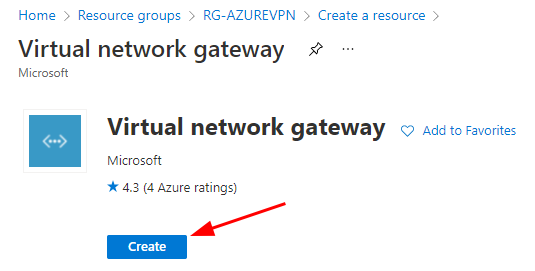
Create virtual network gateway
Creating the virtual network gateway is straight forward. The Basic SKU would be good enough but in this case I picked VpnGW1. Different SKU’s are available but pricing increases every step. A quick view on pricing can be found here.
Note: OpenVPN is not available in the Basic SKU!
3. Create virtual network gateway
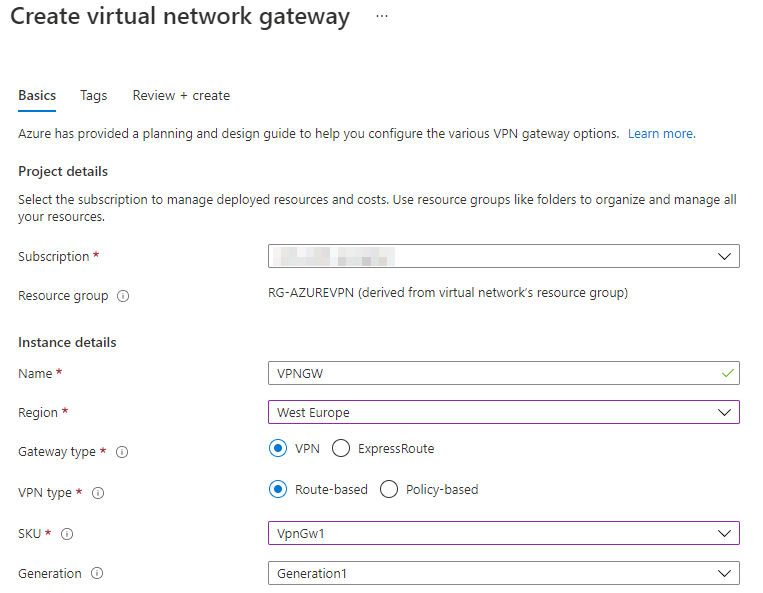
Create virtual network gateway
I assume that there’s no Virtual Network available yet and thus we create one via the Virtual Network Gateway creation wizard. For this demo the default address space and subnet is fine.
4. Create virtual network
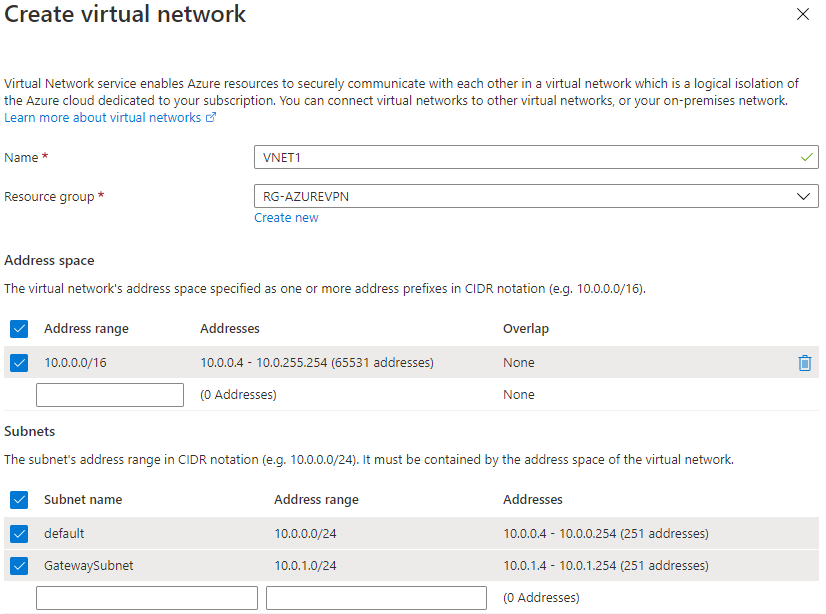
Create virtual network
5. Continue creating the virtual network gateway. Click Review + create to continue.
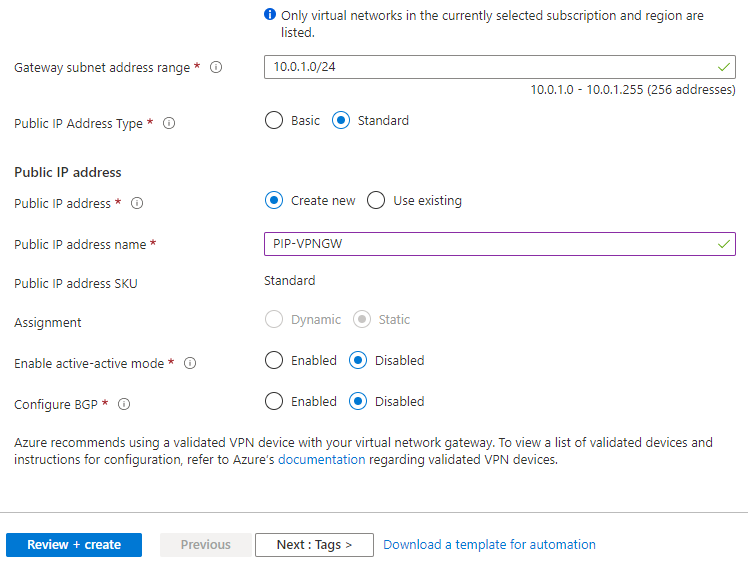
Create virtual network gateway
Here’s a quick summary of the VPN Gateway I’m creating and using for this demo. Click Create and wait until the VPN Gateway is deployed.
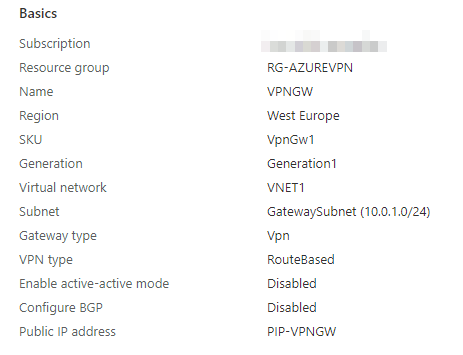
Summary
Note: I’ve seen deployments which took over 45 minutes to complete. I’m not 100 percent sure but if I remember right, this had something to do with registering a new public IP. If u have a public IP already this could be way faster. In my case it took 35 minutes to complete.
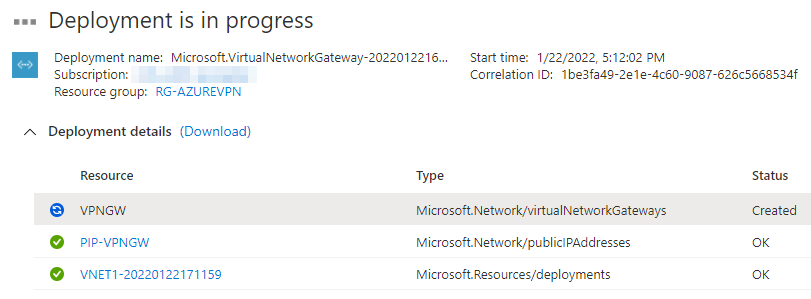
Deployment progress
Azure VPN Enterprise App
First, we have to enable Azure AD Authentication to this Azure VPN Gateway. Therefor we have to add a specific Enterprise App and grant consent to it. Therefor u have to open one of the following URL’s which is depending on the current type of tenant you are using.
6. Open the URL which belongs to your type of tenant and logon with a Global Admin account. Accept the requested permissions.
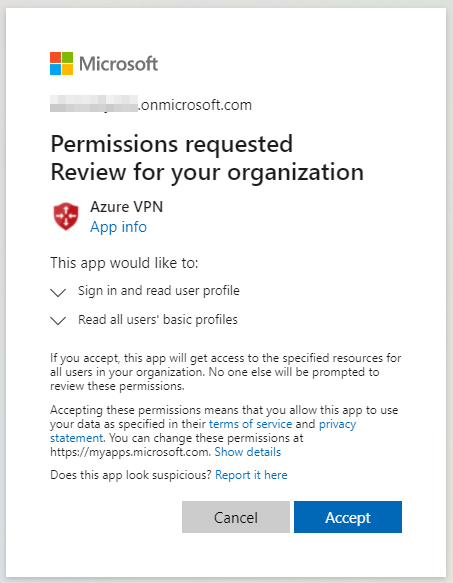
Azure VPN permissions
Once accepted, you should see the following Enterprise App in the Azure portal. Copy the application ID (41b23e61-6c1e-4545-b367-cd054e0ed4b4), we need this in the following step!
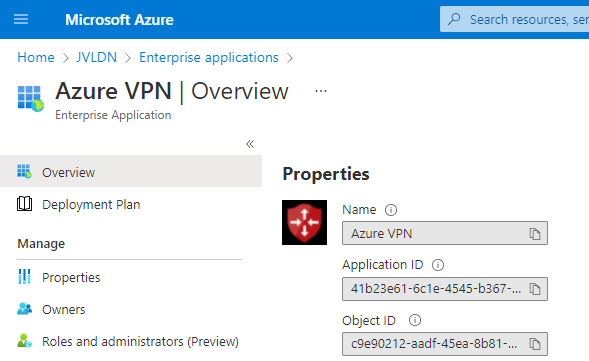
Azure VPN Enterprise App
Point-to-site configuration
7. Open your your Virtual Network Gateway -> Point-to-site configuration -> Configure now
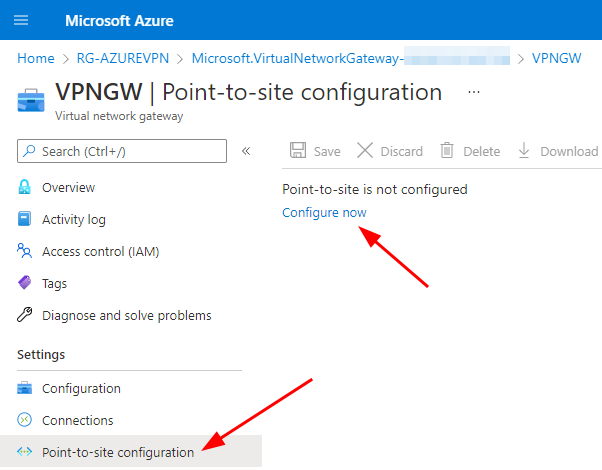
Point-to-site configuration
8. Configure the following settings.
- Address pool: The client VPN connections are receiving an IP in this range.
- Tunnel type: OpenVPN (SSL)
- Authentication type: Azure Active Directory
- Tenant: https://login.microsoftonline.com/9b508669-d87d-\*\*\*\*-\*\*\*\*-\*\*\*\*\*\*\*\*\*\*/ (Tenant ID)
- Audience: 41b23e61-6c1e-4545-b367-cd054e0ed4b4 (Enterprise App ID from step before)
- Issuer: https://sts.windows.net/9b508669-d87d-\*\*\*\*-\*\*\*\*-\*\*\*\*\*\*\*\*\*\*/ (Tenant ID)
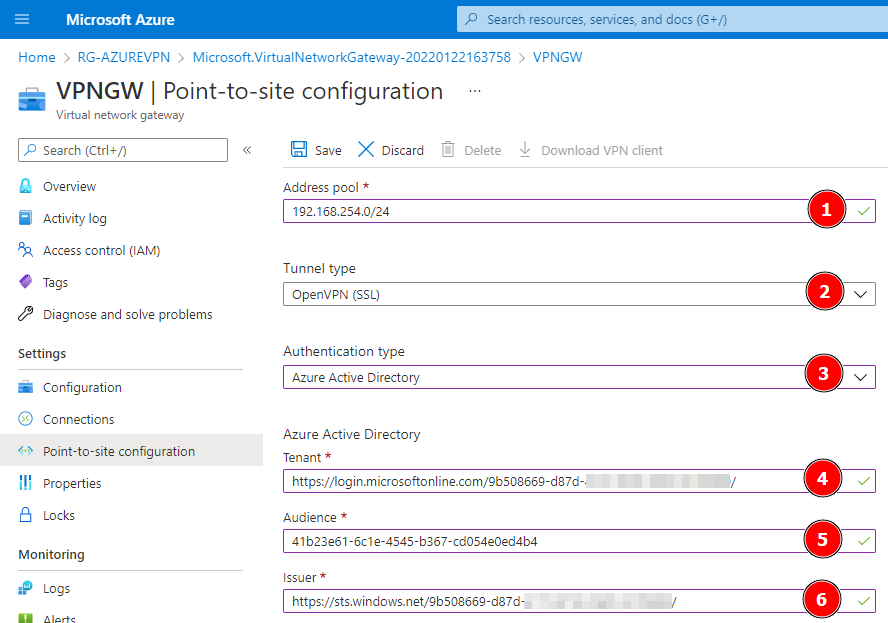
Point-to-site configuration
Deploy the Azure VPN client via Intune / Endpoint Manager
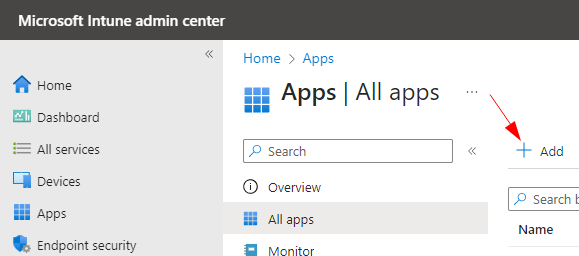
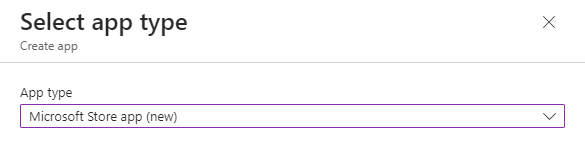
9. Switch to Endpoint Manager / Intune: https://intune.microsoft.com. Add the Azure VPN client which can be found in the new Microsoft Store. Click Add -> Select Microsoft Store app (new).
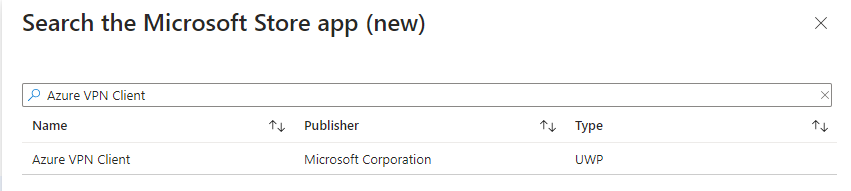
Search for the Azure VPN Client App.
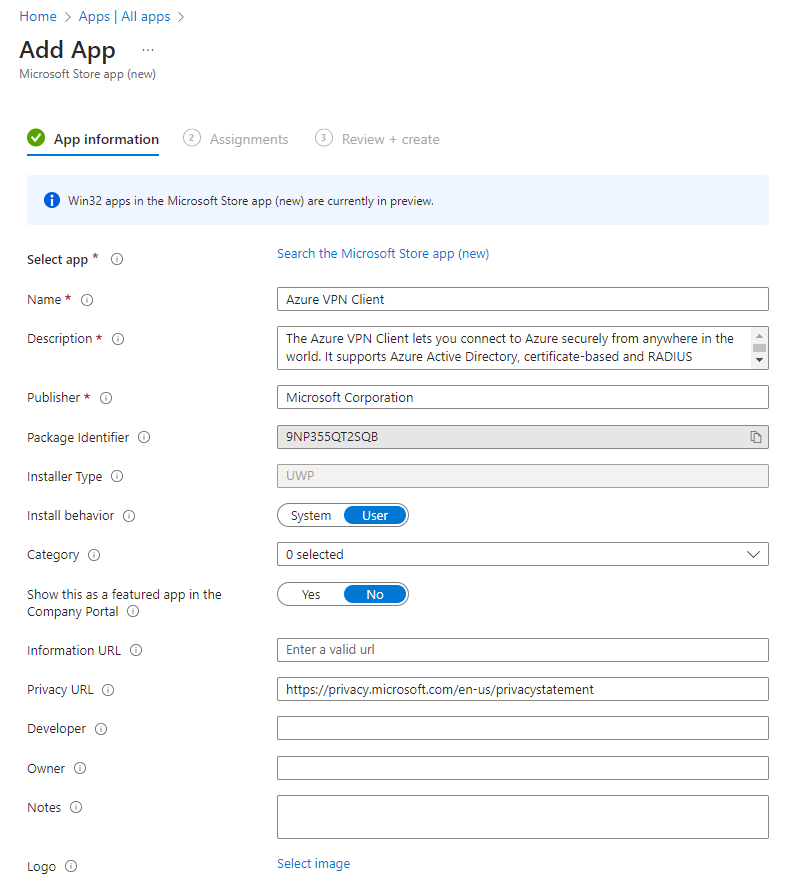
Click Next and assign the application for all devices or a specific group.
Prepare VPN Profile config
The VPN profile is a XML file with specific settings. This XML file is being deployed via Intune. Before we can deploy the XML we have to configure it. I’ll share a custom XML file below which needs to be modified! Read the steps below carefully!
10. Download the VPN Client and unpack the .zip file
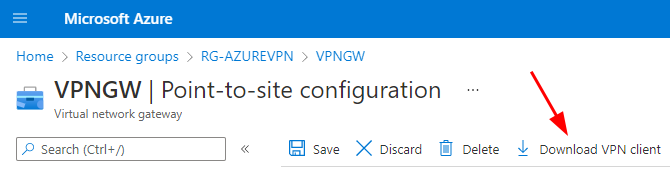
11. Grab my Example VPN Profile from my Github and make the following modifications:
- Line 5: Modify the
setting to the DNS suffix, your DHCP server is sending out to your clients. This will be used to determine if a device is connected to the internal network or external. For example: contoso.local. - Line 9: Modify the
setting. This value can be found in the Generic/VpnSettings.xml file which is in the downloaded .zip file from step 11. - Line 18: Modify the
setting https://sts.windows.net/TENANTID/. This can Also be found in (see step 8) - Line 19: Modify the
setting https://login.microsoftonline.com/TENANTID/. This can Also be found in (see step 8) - Line 31: Modify the
setting. This is the VNET name which is created in step 4. For example: VNET1. - Line 41: Modify the
setting. This value can be found in the AzureVPN/azurevpnconfig.xml file which is in the downloaded .zip file from step 11. - Line 46: Modify the
setting. This value can be found in the AzureVPN/azurevpnconfig.xml file which is in the downloaded .zip file from step 11. - Line 50: Modify the
setting. This value can be found in the AzureVPN/azurevpnconfig.xml file which is in the downloaded .zip file from step 11.
Save your custom VPN profile as .XML and keep it somewhere safe! 🙂
Deploy VPN profile via Intune / Endpoint Manager
12. Switch to Endpoint Manager / Intune: https://intune.microsoft.com -> Devices -> Create Profile
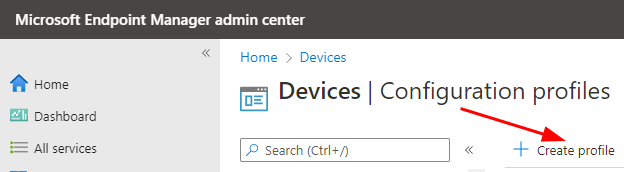
Create profile
13. Pick Windows 10 and later as platform and Templates as profile type. Click template name Custom.
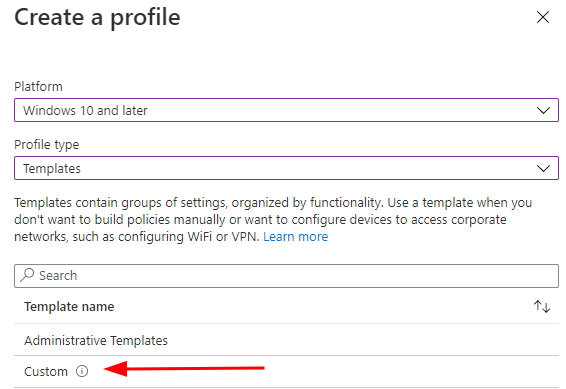
Custom profile
14. Give your profile a name
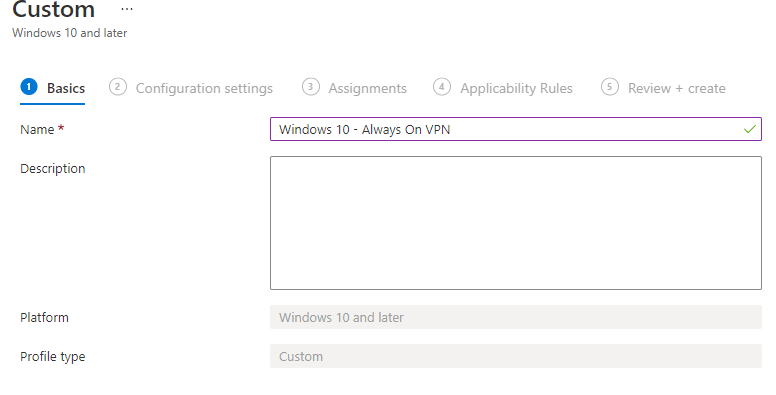
Configuration profile
15. Create a new OMA-URI Setting. I’m not sure if spacing is allowed in the fifth section. We have used – within all words. This is the profile name which is shown in the end-user device and Azure VPN client.
- Name: AO VPN Azure AD
- Description: Optional
- OMA-URI: ./User/Vendor/MSFT/VPNv2/Contoso-AO-VPN/ProfileXML
- Data type: String (XML file)
- Custom: XML: Import your VPN Profile XML file created in step 11.
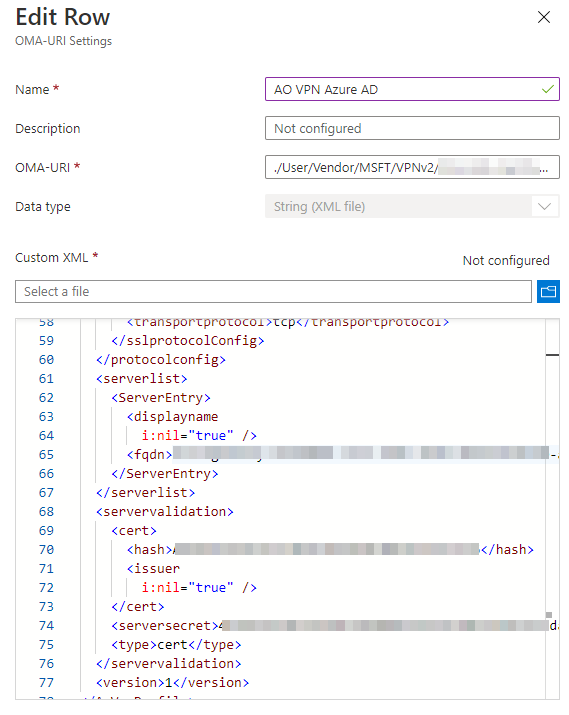
16. Assign the configuration profile to a user group and wait until the profile is deployed.
Endpoint – User Experience
While the Azure VPN Client and VPN profile are deployed into the Endpoints, users will be required to follow the following steps.
17. Authentication with Azure AD (identity provider) is required. Click continue.
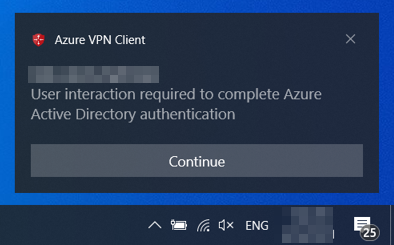
Azure VPN Client
18. The VPN connection will now show disconnected. Click Connect.
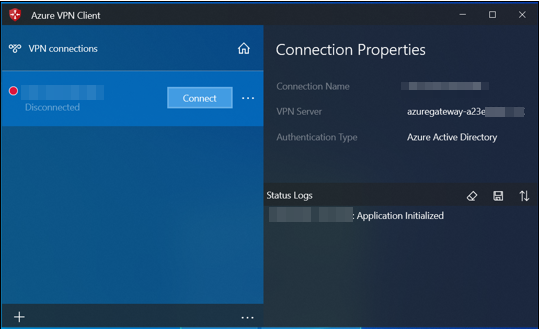
Azure VPN Client
19. Select the current logged on user account. Accept the MFA request (when CA/MFA is configured). If you don’t get a required MFA response you should have a look into this article. I recommend MFA for this kind of connections/apps.
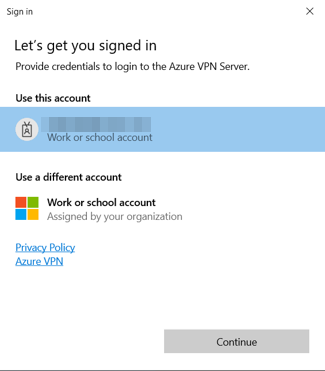
Accept MFA
20. When everything went ok, the connection will establish and stays connected. Keep in mind that the VPN connection will disconnect immediately if your DNS suffix matches the
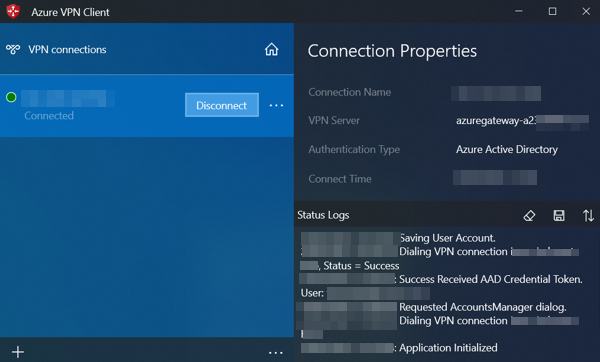
Azure VPN Client
Connection monitoring
If your endpoints are connected to the Azure VPN Gateway, they will report their current IP addresses into the Point-to-site configuration dashboard.
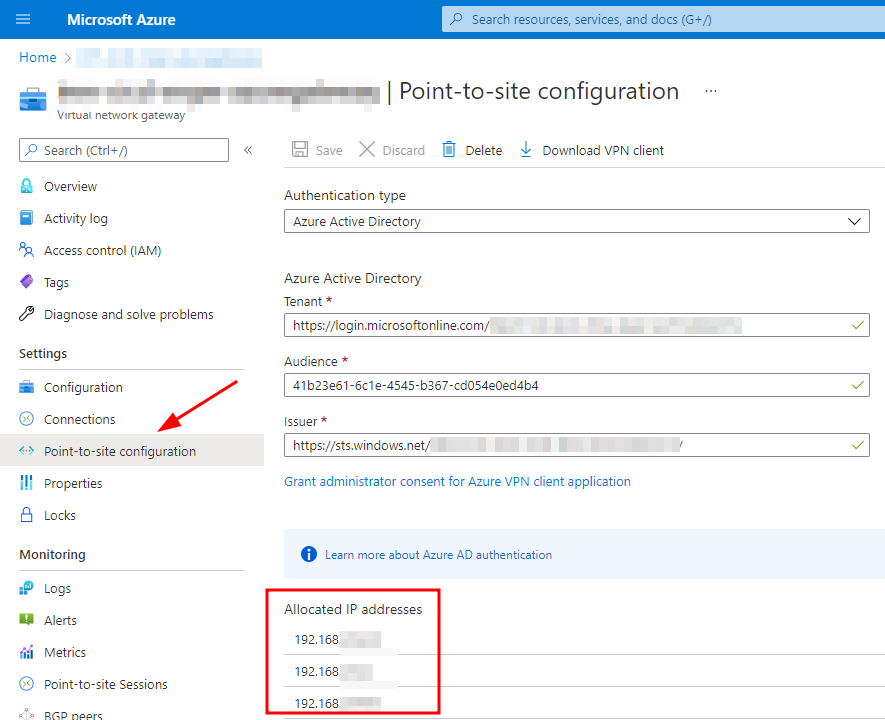
Connection monitoring
Written by Joey Verlinden
Back to all articles